Automated Regulatory Reporting: How to Build a Compliant-by-Design System
- 10Pearls Editorial Team
- 14 min read
Summary
Automated regulatory reporting enables organizations to reduce compliance risks, improve audit readiness, and streamline reporting processes. Compliant-by-design systems embed regulatory requirements into workflows from the beginning with built-in governance, validation, and automation.
The compliance environment is rapidly changing because of technological advancements, resulting in heightened compliance risks. Regulatory, legal, and governmental uncertainty, along with geopolitical risks, AI use, and increased regulatory requirements, are all putting pressure on compliance, increasing the need to demonstrate value and manage new kinds of risks.
Compliance teams now need to collect and report on new metrics to meet these dynamic demands. This data, however, is spread across several business units and third-party networks. A recent report indicates that tools for proactive data analysis, surprise audits, hotlines, and financial statement audits can reduce fraud losses and detection time by at least 50%. This calls for compliance-by-design systems along with the tools that can automate regulatory reporting.
What is automated regulatory reporting?
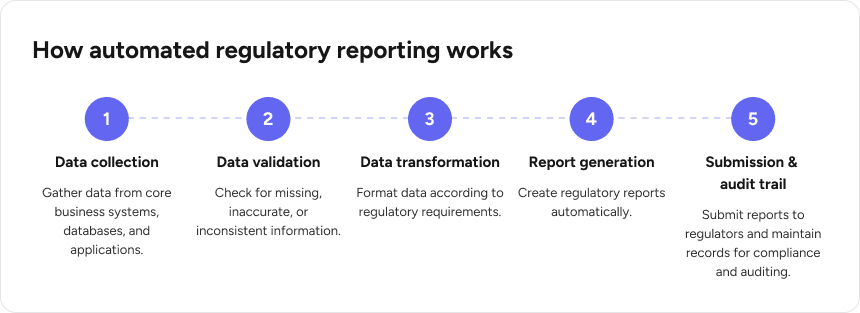
The use of technology to streamline data collection, validation, transformation, and submission of required reports to regulatory authorities, with minimal manual effort and to ensure timely compliance, is called automated regulatory reporting. It reduces compliance risks and minimizes errors.
Compliance reports such as financial statements, transactional data, liquidity metrics, etc., are often shared with regulatory bodies such as central banks, financial conduct authorities, and industry-specific regulators. As regulations become more complex and reporting volumes increase, automated regulatory reporting provides consistency to meet the demands in a structured way.
Why manual regulatory reporting breaks
In today’s landscape, the sheer volume of data makes it extremely inefficient for organizations to conduct manual reporting. It is very time-consuming and incurs higher costs and more human labor. It requires tedious tasks like going through documents to collect data, reconciling it in spreadsheets, performing calculations, filling in documents to prepare reports, running audit trails, etc. It also increases the likelihood of errors. Whereas automated regulatory reporting allows this process to be completed in near real time or within a few hours, rather than days.
Difference between manual & automated regulatory reporting
| Dimension | Manual reporting | Automated reporting |
|---|---|---|
| Data collection | Manual extraction from multiple siloed systems | Automated pipelines from governed source systems |
| Validation | Spreadsheet formulas; human spot-checks | Rule-based validation engine with exception management |
| Audit trail | Fragmented; difficult to reconstruct | Immutable, end-to-end lineage from source to submission |
| Regulatory change handling | Ad hoc; manual updates to templates and formulas | Versioned rules engine; change-impact analysis |
| Filing deadlines | Deadline-driven crunch; limited buffer for review | Scheduled automation with buffer for review and approval |
| Cost of error | Regulatory fines, resubmission, reputational risk | Errors caught pre-submission; remediation cost minimized |
What compliant-by-design means?
The idea behind compliant-by-design systems is that we should build systems that naturally produce compliant outcomes. It is an approach in which all requirements, such as regulatory, legal, security, privacy, and governance requirements, are translated directly into compliant processes and systems from the beginning. All the controls, policies, and validation rules are embedded in the workflows to automate monitoring and reporting, ensuring that requirements are continuously met and regulatory adherence is maintained.
How to build a compliant-by-design reporting system
The compliance process has shifted from reactive to proactive by anticipating and mitigating risks in real time, achieved by developing systems that are compliant-by-design. For automated compliance reporting, compliance must be embedded in the architecture: the data models, workflows, APIs, validation engines, and event-processing logic. For regulated industries like financial systems and banking institutions, a regulatory reporting system can be structured around the following capabilities.
Conduct a gap analysis
The compliance environment is always evolving, so it's important to evaluate your current standing in terms of current policies, procedures, and controls against industry standards.
Unified data foundation & governance
Collect data from different business units to develop a single source of truth for reporting and analysis. Establish data integrity and security by mapping data lineage and managing its availability and usability across the organization.
Implement automated data validation
Check the data for errors without manual intervention using predefined business rules and AI algorithms.
Standardize reporting logic
Minimize interpretation by aligning data collection, calculating formulas, and visual formatting across the organization.
Automate report generation and approval workflows
Map out the process, determine approval stages, set predefined templates and roles, and schedule regular distribution of reports to relevant stakeholders and regulators.
Enable traceability & auditability
Set up processes for reliable tracking and verification of actions, transactions, and data states within a system.
AI & agentic automation, governed
Use AI, ML, and agentic automations to detect anomalies, trends, and regulatory changes, with ai governance services defining where human oversight is required.
Secure sensitive data
Set up a multi-layered defense with strong encryption, strict access controls, and regular data backups.
Monitor & adapt to regulatory change
Automate tracking of new and evolving regulatory requirements to ensure adherence to laws and regulations.
Build vs. buy vs. hybrid
Choosing the right compliance reporting software requires considering a number of factors such as time-to-market, customization needs, and regulatory complexity, etc. The right approach, whether building, buying, or adopting a hybrid model, depends on your organization’s goals, existing technology landscape, and compliance obligations.
Before making a decision, it’s important to evaluate both immediate requirements and future needs to ensure the solution can adapt as regulations and business priorities evolve.
Need help determining the right approach? Our compliance and technology specialists can assess your requirements, recommend the best-fit strategy, and support implementation, integration, or custom development to accelerate your compliance reporting initiatives.
The table below compares the key considerations for build, buy, and hybrid compliance reporting approaches.
| Approach | Best for | Pros | Cons |
|---|---|---|---|
| Buy | Standardized, non-differentiating compliance needs (e.g., SOC 2, GDPR, AML) | Faster time-to-market, vendor manages regulatory updates, economies of scale | Rigid workflows, vendor lock-in, recurring licensing fees |
| Build | Organizations with highly unique operational edge cases and strict data residency needs | Total control over architecture, customized integrations, supports competitive advantage | High initial and ongoing maintenance costs, massive internal IT burden |
| Hybrid | Large or heavily regulated firms with complex internal systems | Flexibility to customize critical processes while automating standard tasks | Integration complexity, potential conflict between vendor and custom tools |
Benefits of automated compliance reporting
The enterprises that implement automated compliance reporting experience transformation across multiple dimensions. Continuous monitoring provides greater visibility into risks and reporting processes, helping organizations identify issues earlier and improve compliance oversight.
Leadership confidence & trust
Provide leadership with accurate, timely insights that support confident decision-making.
Expanded risk visibility
Get a wider view of risks across transactions, operations, and business functions that traditional audits may overlook.
Proactive risk management
Identify emerging risks earlier through continuous monitoring and faster issue detection.
Real-time performance insights
Give board members access to current compliance data instead of waiting for quarterly audit reviews.
Improved operational efficiency
Reduce manual effort and free audit teams to focus on higher-value analysis & decision-making.
AI & agentic automation in automated compliance reporting
AI & agentic automation in automated compliance reporting Most compliance teams reach this stage through agentic ai development services rather than building agent orchestration in-house, because the governance layer is harder than the agents. Agentic AI refers to systems or agents that can act autonomously with little to no human intervention, make context-aware decisions, and independently pursue goals
Agentic AI, the latest addition to the AI family that transforms compliance from mere task execution to a strategic risk-detection process. It changes how organizations approach compliance by using sophisticated machine learning models, natural language processing, and intelligent decision-making capabilities.
That reach depends on ai integration services: agents query ERPs, cloud platforms, and access management tools to validate controls and put audit-ready documentation together.
AI agents can keep a constant eye on global regulatory databases and interpret overlapping frameworks to update internal controls automatically. These frameworks can be the likes of GDPR, Basel III, HIPAA, etc.
Agentic AI takes the anomaly detection process to the next level by resolving the issues autonomously. Instead of just raising an alert, they can execute mitigation workflows, generate summaries, and assign tasks to process owners.
FAQs about automated regulatory reporting
What is automated regulatory reporting?
Automated regulatory reporting refers to the use of technology and software to streamline data collection, validation, transformation, and submission of required reports to regulatory authorities with minimal manual effort.
What does "compliant-by-design" mean?
With a compliant-by-design approach, we develop systems designed to generate outputs that meet regulatory requirements. Instead of treating compliance as a final review step, organizations embed controls and reporting requirements directly into the underlying architecture, workflows, and data models.
How do you automate regulatory reporting?
Automating regulatory reporting starts with bringing reporting data into a single trusted source. From there, validation rules & reporting logic, approval workflows, and audit trails are used to generate and review reports automatically. Ongoing monitoring helps ensure reports remain consistent and aligned with the latest regulatory requirements.
What data and controls does a compliant reporting system need?
A compliant reporting system needs accurate data from the systems used across the business. It should also include controls such as data checks, user access controls, approval processes, and audit records to support regulatory reviews.
Can AI be used for regulatory reporting safely?
Yes, AI can support tasks such as data validation, monitoring, and exception handling. However, organizations should have clear rules for how AI is used, with people reviewing and approving any decisions or regulatory submissions.
Which industries need automated regulatory reporting most?
Automated regulatory reporting is most common in banking, capital markets, insurance, fintech, and payments. These industries face frequent reporting requirements and manage large amounts of data, making manual reporting difficult and time-consuming. With extensive experience in highly regulated industries, 10Pearls helps organizations modernize reporting processes while meeting evolving compliance requirements.
Build reporting systems that are compliant from the start!
Regulatory requirements are growing in volume and complexity. Catching up after the fact is expensive. As an artificial intelligence software development company working in regulated markets, 10Pearls’ fintech software development services teams help banks, fintechs, and capital markets firms design and implement automated regulatory reporting systems with the data foundations, validation controls, and auditability built in from day one.
Related blogs
Fintech
Banking as a Service (BaaS): How It Works
Learn what Banking as a Service (BaaS) is, how it powers embedded finance, and how non-banks integrate accounts, cards, payments,...
Fintech
Synthetic Identity Fraud Detection and Prevention
Synthetic identity fraud is the fastest growing financial crime in the US. Understanding why that is and what its life...
Fintech
How AI creates value with open banking data
Every fintech company with an open banking license in Saudi Arabia must build the basic infrastructure to receive open banking...
Fintech
Key strategies for navigating 1033 compliance in finance
In its final rule, implementing section 1033 of the Dodd-Frank Act, the Consumer Financial Protection Bureau (CFPB) defined requirements that...
Fintech
Explore common misconceptions of agile fatigue
Within the past few years, there has been relative fatigue in many organizations in adopting and implementing Agile practices, processes,...
Fintech
Fintech, or Financial Technology, is transforming financial services. The fintech industry has seen explosive growth over the past decade, and...
Fintech
Identify leading fintech software development partner to create secure, scalable, and innovative applications customized to meet your specific financial technology...
Fintech
Generative AI has revolutionized financial management, bringing about a new standard for efficiency and precision. Processes like financial analysis and...